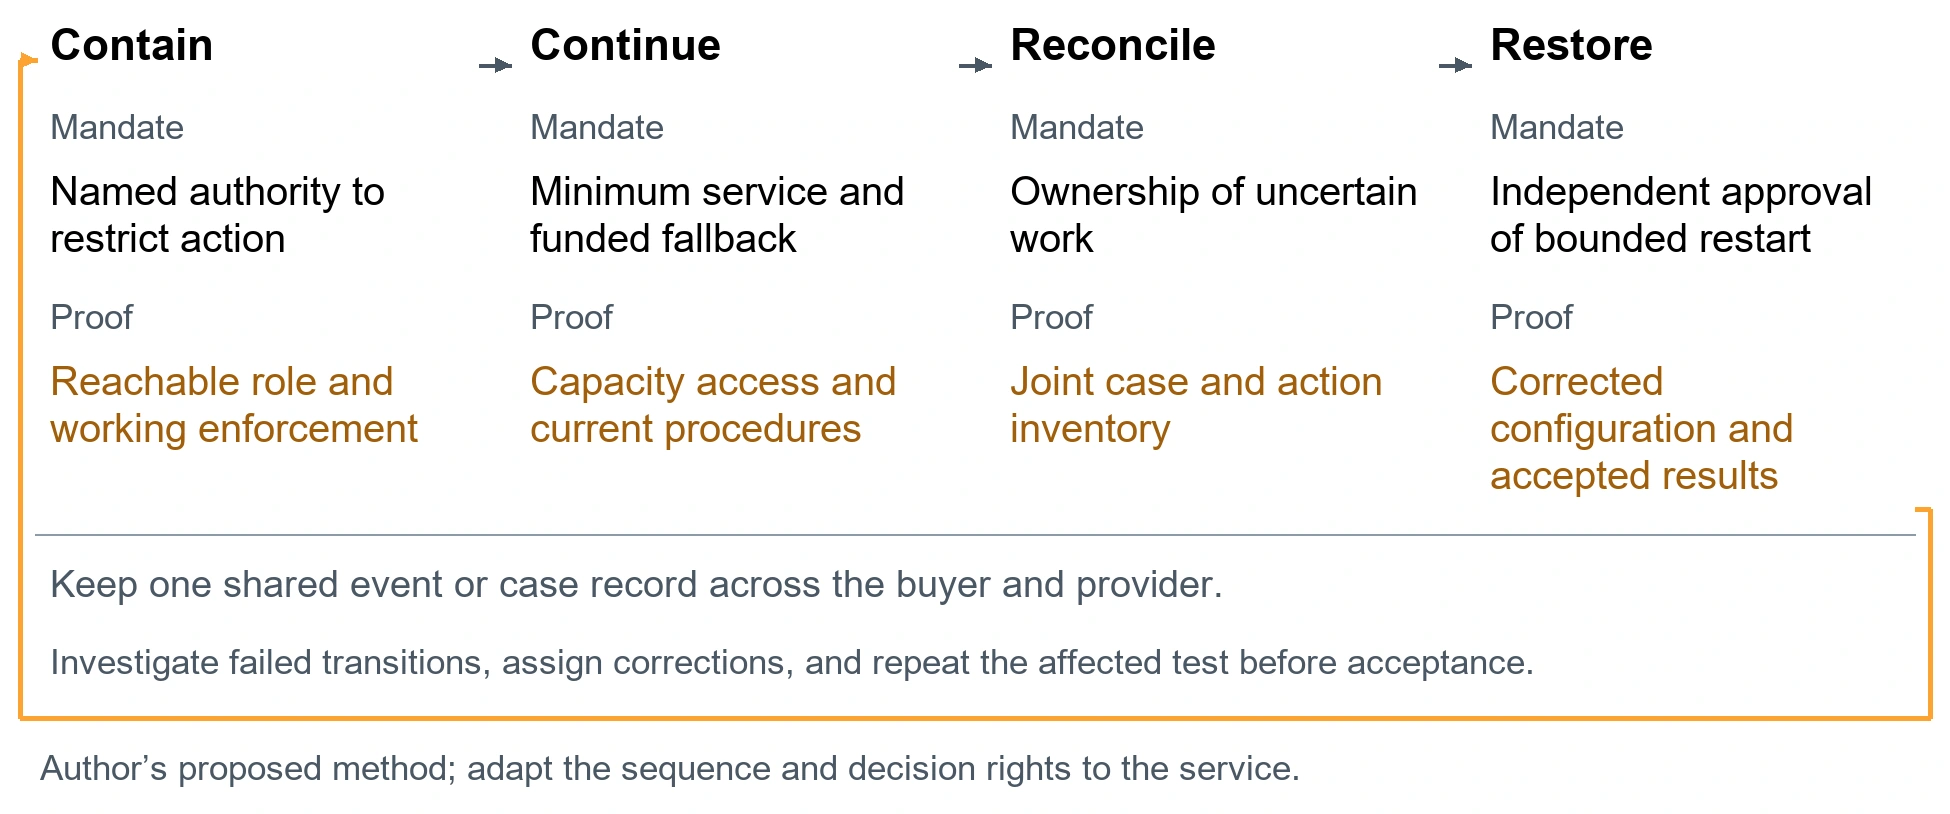
The chief operating officer should establish a joint containment and restoration mandate for material agentic services. The mandate should give named roles the authority to impose proportionate restrictions when defined harm is suspected. It should also assign responsibility for preserving service, reconciling uncertain work, and deciding when normal operation can resume.
A contractual right to stop an agent does not establish that reachable staff can exercise it or that a business service can survive the interruption. The study reports uncertainty over stopping authority and out-of-hours escalation. Those accounts support examining the authority structure, while leaving the effectiveness of any particular mechanism to direct testing.1
The executive decision should precede disagreement about fault. A buyer and provider may each believe the other caused an incident. The operating mandate should permit agreed protective action while the investigation proceeds, with commercial allocation resolved through a separate process. Otherwise, a liability dispute can obstruct containment.
Stopping an agent can remove a source of harm and create a service gap at the same time. A payment queue, customer response obligation, or essential operational process may continue to require attention. The mandate should identify the minimum acceptable service and the alternatives available when autonomous execution is restricted.
The provider should specify which capabilities remain usable in a restricted mode. The buyer should confirm who can operate the fallback, with what access, information, capacity, and supervision. A manual route described in a continuity document may no longer be viable after staff, systems, or process knowledge have changed.
Consider a hypothetical customer-account service producing unauthorized amendments. The first action may be to block writes, while retained staff inspect affected cases and continue permitted inquiries. The correct design depends on the service. Executives should require that choice to be made and rehearsed rather than prescribe a universal shutdown.
Figure 1 proposes a mandate with different decisions for restriction, continuity, reconciliation, and restart. The incident commander should coordinate those decisions, while domain owners retain authority over risks they are responsible for accepting. Restart should require affirmative approval; it should not occur automatically when a provider reports that the agent is available.
The mandate should identify the information needed for each decision and the escalation path when evidence is incomplete. A temporary restriction can be justified by credible exposure before every fact is known. The decision record should preserve that uncertainty and the reason the chosen action was proportionate.
The allied guidance emphasizes containment, resilience, and human control. The executive extension proposed here is to connect those security measures to continuity of the contracted business outcome. The guidance does not certify the fallback or determine the organization’s acceptable interruption.2
The buyer should fund the retained capabilities it expects to use. Staff availability, current procedures, access rights, data export, and queue reconciliation require maintenance. A provider cannot guarantee restoration if the buyer’s required approval team or replacement system is unavailable. Those dependencies belong in the service agreement and continuity plan.
The study’s fragmented visibility accounts identify a further obstacle: the firms may not share enough information to establish what happened. The mandate should require a joint action inventory covering completed, failed, uncertain, and outstanding work. It should distinguish the agent’s intended action from the state observed in the receiving system.3
Evidence access should remain effective during dispute and exit. The buyer needs records necessary for containment, investigation, customer remediation, and applicable reporting. Privacy, secrecy, and security constraints should shape the access design beforehand, rather than emerge as a reason that no useful evidence can be provided.
Restoration should follow evidence that the immediate cause is contained, the approved configuration is deployed, permissions are appropriate, and uncertain work is reconciled. Begin with bounded operation and independently checked outcomes. A technically successful restart can still leave incomplete cases or customer harm unresolved.
The executive should also resolve veto authority. Security may consider the technical fault contained while operations still cannot reconcile customer cases. Restart should wait for the conditions assigned to both functions, with a named senior route for resolving disagreement. The mandate should state who can accept the remaining exposure and what evidence that person receives. It should not allow the provider’s restoration announcement to remove an unresolved buyer obligation.
Mayer Brown’s agentic contract analysis treats performance dependencies, liability, and exit as linked commercial issues. Applied to a managed service, the lesson is to specify cooperation and continuing duties during recovery. The parties should not discover only after an incident that necessary assistance is excluded from the contracted service.4
For global operations, distinguish the shared containment decision from local legal reporting and customer duties. EU, UK, Swiss, and US entities may have different obligations and clocks. Local accountable officers should receive the common incident evidence and determine what their entity must do.
The executive sponsor should commission a scenario that tests harmful action, unreachable contacts, restricted operation, uncertain transaction state, and restart. A technical rehearsal can demonstrate enforcement; a tabletop can examine decisions and communications. Management should state clearly which elements were tested and which remain assumptions.
The board should receive unresolved gaps that threaten acceptable service or prevent containment. Continuation should depend on a funded correction plan and proportionate restrictions. The executive mandate is complete when the firms can demonstrate who decides, what stops, how work continues, and which evidence permits restoration.
The study is a nonrepresentative cross-section of 850 vendor delivery-team respondents on 150 engagements serving Tier 1 financial institutions, collected during January–June 2026. Neither banks nor vendors corroborated the accounts. It establishes reported experience, not causation, legal breach, or market prevalence. Its application here is a mechanism to investigate, not an estimate of conditions in other industries. The author-supplied version 1.8.2 is dated November 1, 2026 and is cited as a forthcoming manuscript consulted October 23, 2026.5
This is an analytical decision paper based on the supplied study and selected primary public sources checked through October 23, 2026. The original contribution is an executive containment and restoration mandate connecting stop rights to funded continuity and business acceptance. The proposed method has not been independently validated. Legal requirements depend on the entity, activity, jurisdiction, and effective provisions; supervisory observations, research, and professional commentary have distinct authority.