The executive sponsor should approve the business authority of an outsourced agent separately from the decision to buy the service. Access to a tool does not explain which actions the provider may take on the buyer’s behalf. A contract description such as case resolution can conceal materially different powers to read, recommend, amend, commit, or delegate.
The proposed authority mandate records the action, protected resource, permitted purpose, operating conditions, duration, and accountable buyer. It also identifies the provider principal exercising that authority. An agent should receive only the permissions needed for the approved task, with consequential actions enforced by systems that the agent cannot instruct to waive the restriction.
NIST’s February 2026 identity initiative identifies authorization, auditing, and non-repudiation as agent-specific design questions. It is a concept-paper initiative, not a mandatory finished standard. Executives should require their teams to answer those questions for the actual service rather than accept a supplier’s general identity claim.1
A hypothetical procurement agent may have technical access to a purchasing system but authority only to prepare orders below an approved threshold for named categories. The executive mandate should state whether it can commit the buyer, change a supplier, or authorize another agent. Technical teams should then translate those decisions into enforceable permissions.
The study’s accounts of staff and shared credentials reveal a practical risk: the recorded identity may not identify the actor or the authority used. They are vendor-team reports, not verified access assessments. Their executive implication is to demand a clear link between the approved business task and the identity performing each consequential action.2
A named buyer employee should not become the implied source of every agent action because a provider borrowed that employee’s account. Management should provide a supported route for agent identities and escalation when access is delayed. The alternative should be an authorized fallback, with its service and cost implications visible.
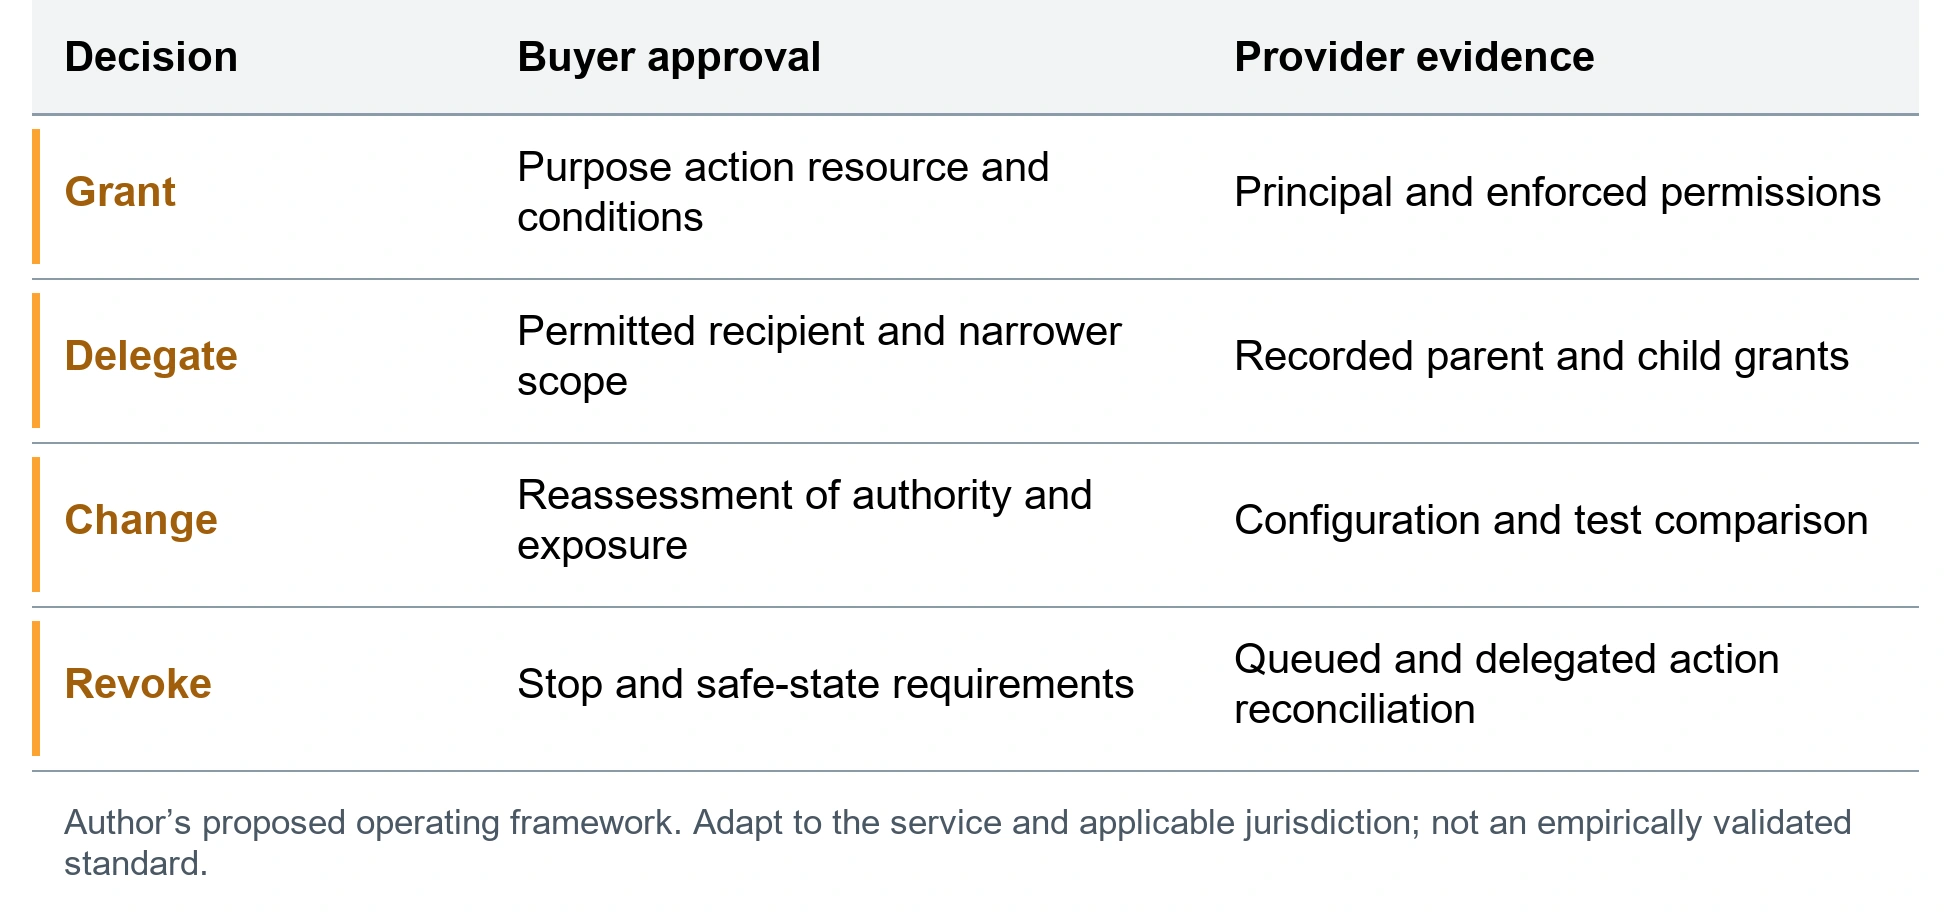
Figure 1 sets out four authority decisions. Permission to perform a task should not automatically include permission to delegate it. The mandate should specify allowed recipients, narrower child permissions, expiry, and the evidence linking every child action to the original grant. A provider must disclose when another firm enters the delivery chain.
The allied agent-security guidance recommends bounded permissions, recorded grant chains, and controls against unapproved delegation. Those recommendations support the design direction; they do not determine what authority a particular enterprise can lawfully delegate. The buyer’s business and legal functions must make that decision for the service.3
A delegation should fail closed when its parent expires or is revoked, subject to an approved safe-state design. The firms should test whether queued actions, delegated credentials, and external commitments follow the revocation. An executive should receive the residual exposure, including actions that have already become irreversible.
The buyer needs enough evidence to establish who acted, under which grant, on what resource, and with what result. It need not obtain every provider prompt or proprietary implementation detail. Define a minimum action record with reliable timestamps, configuration references, authority identifiers, and the downstream state needed for verification.
The study describes agent actions visible only within each firm’s tools. This fragmentation matters because a provider log can prove a request was sent while the buyer’s system shows a different result. Reconcile both sides for consequential actions rather than treating either party’s success flag as the complete record.4
The chief information security officer should agree how evidence is protected and shared. Detailed logs can themselves expose personal information, secrets, or privileged business data. Access restrictions and retention should preserve the required accountability without creating an uncontrolled second repository.
Expanding a tool list, changing a resource, or enabling a new delegation route should reopen the authority decision. A model update may also change behavior without changing permissions. Management should require a change assessment that explains whether the approved task, control effectiveness, or potential consequences have changed.
The approval record should include an authority holder who remains accountable when the agent changes. Replacing one model or orchestrator should not silently transfer the power to commit the buyer to a different provider principal. Require a continuity check of the grant, enforcement points, evidence, and revocation path. This is especially important where the service uses several agents but the buyer has approved only one organization and a defined set of actions.
Mayer Brown’s governance analysis recommends checkpoints and least privilege for agents. The buyer-provider mandate proposed here adds explicit ownership at the organizational boundary: who can grant authority, who enforces it, who observes actions, and who can withdraw it. These decisions should appear in the operating schedule as well as the technical configuration.5
Global operations should use a common authority vocabulary with local legal annexes. EU, UK, Swiss, and US entities can face different constraints on commitments, data use, and oversight. The mandate should identify the legal entity whose authority is exercised rather than assume a group-wide service account represents every entity equally.
The executive approval should require a demonstration of normal execution, denied excess authority, and revocation during unfinished work. Management should document what stops, what continues, and what requires recovery. A failed revocation test should restrict the affected authority until the two firms can explain and correct the failure.
The executive decision is whether a defined grant can be enforced and withdrawn across the complete service. Approve the smallest authority that supports the business outcome, fund the necessary identity and evidence functions, and expand only when tests support the additional exposure. The mandate should remain accountable to a named buyer executive.
The study is a nonrepresentative cross-section of 850 vendor delivery-team respondents on 150 engagements serving Tier 1 financial institutions, collected during January–June 2026. Neither banks nor vendors corroborated the accounts. It establishes reported experience, not causation, legal breach, or market prevalence. Its application here is a mechanism to investigate, not an estimate of conditions in other industries. The author-supplied version 1.8.2 is dated November 1, 2026 and is cited as a forthcoming manuscript consulted October 23, 2026.6
This is an analytical decision paper based on the supplied study and selected primary public sources checked through October 23, 2026. The original contribution is a four-part executive authority mandate that connects organizational permission to enforceable agent grants. The proposed method has not been independently validated. Legal requirements depend on the entity, activity, jurisdiction, and effective provisions; supervisory observations, research, and professional commentary have distinct authority.